Sandboxing: RUSTSEC-2026-0367 + CVE-2026-115905 · live demo
You can't execute
what you don't have.
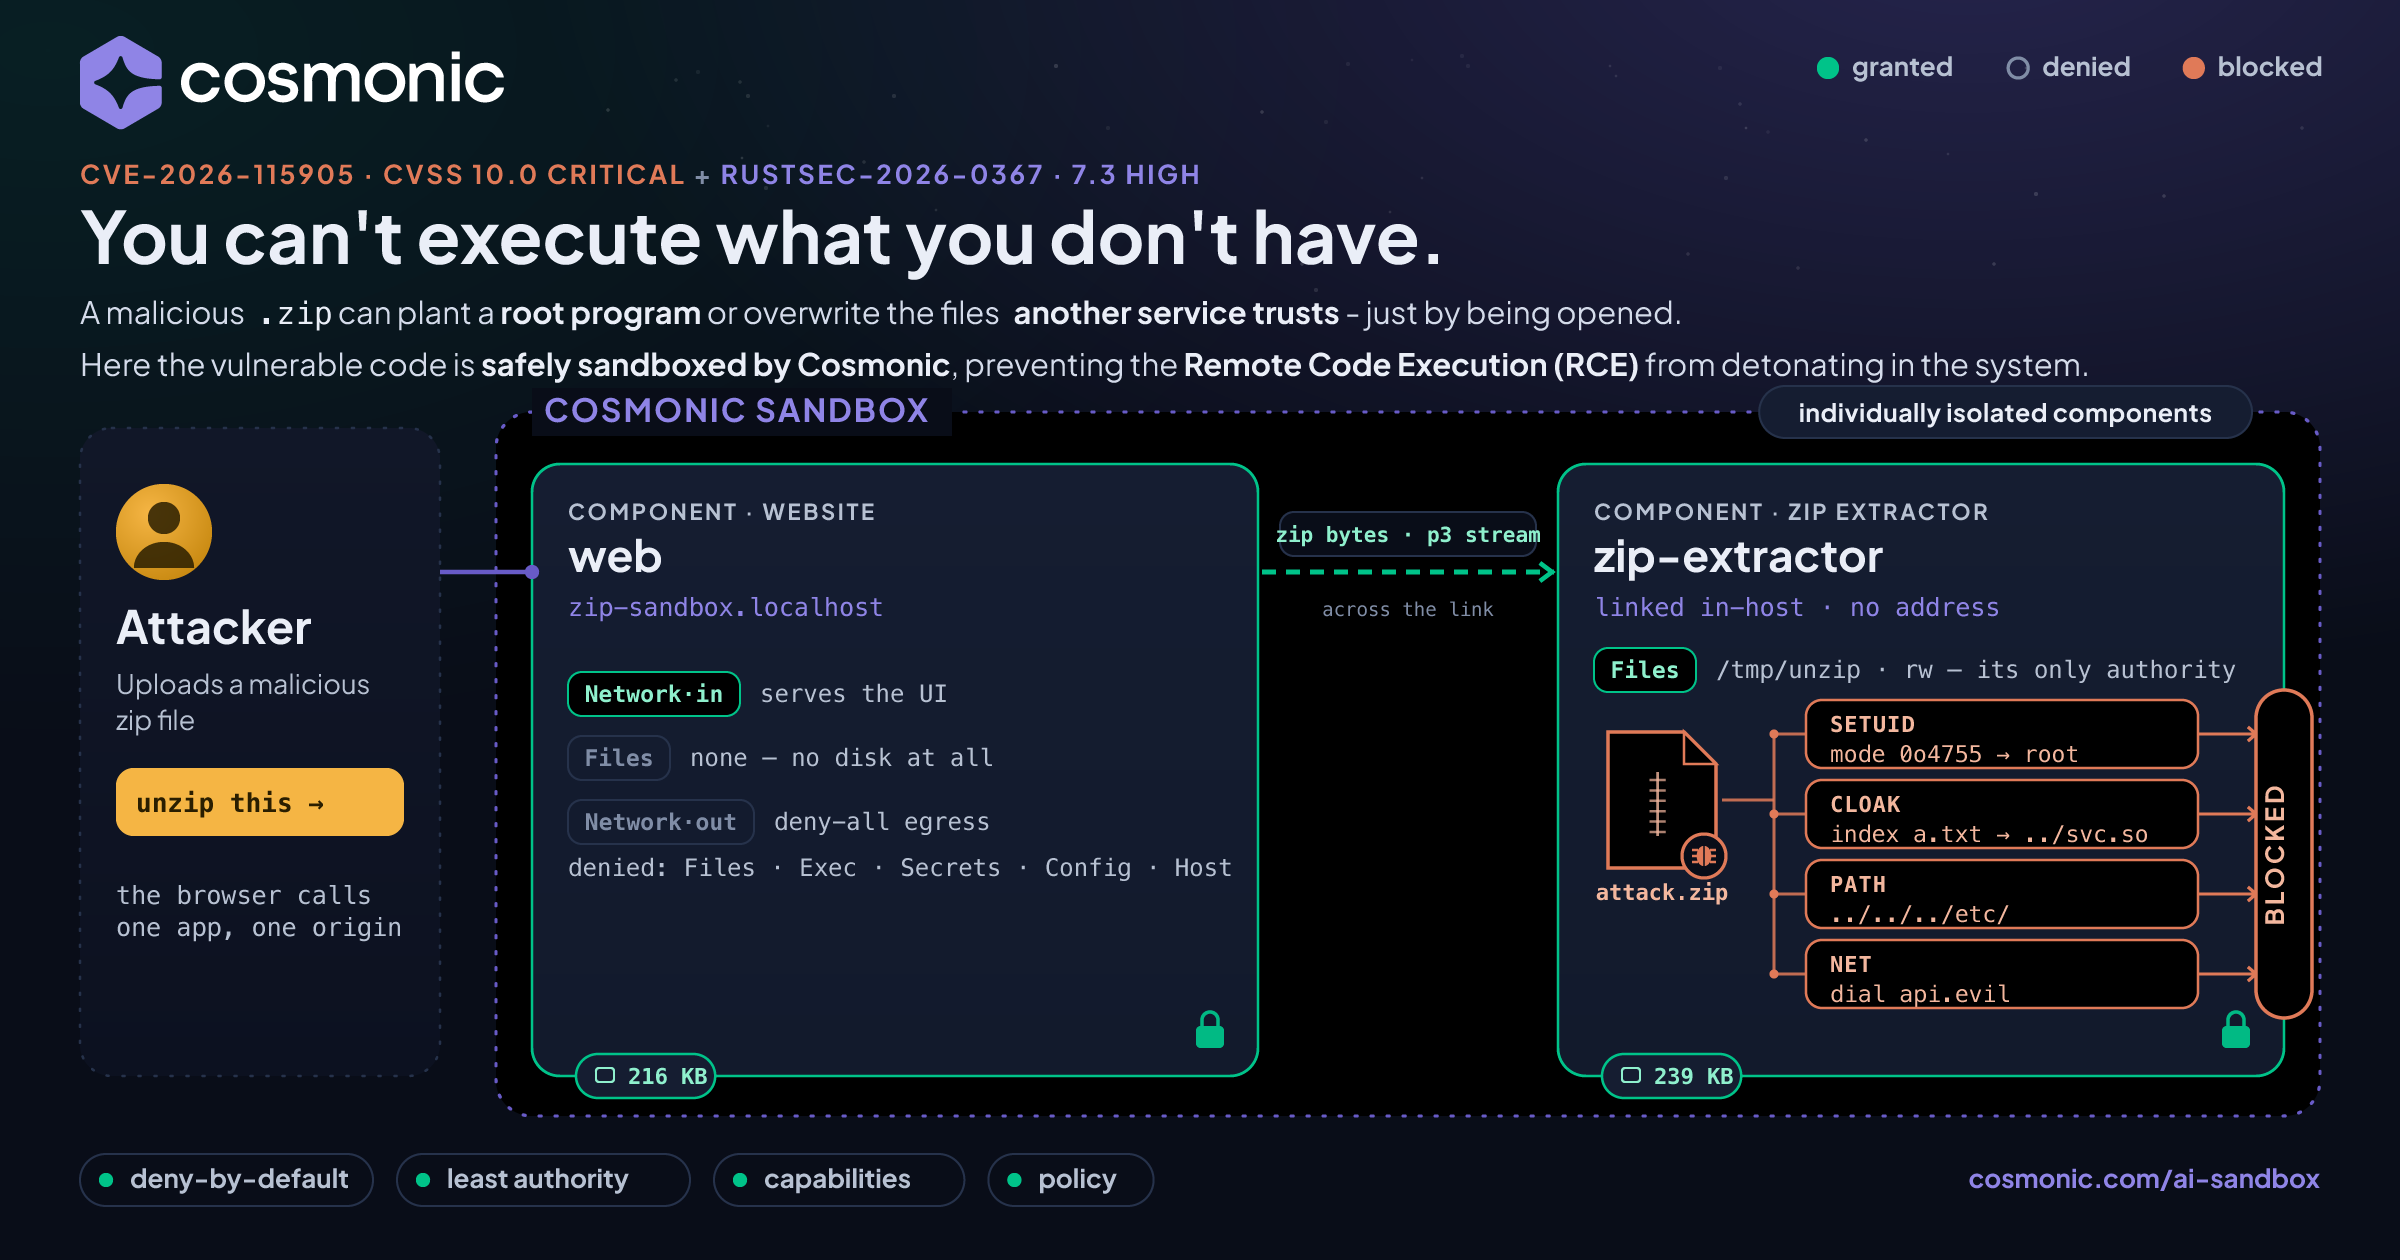
An attacker can craft a malicious .zip file that runs with root powers — or silently overwrites a file another service trusts — just by being opened. Two real CVEs, one library, a week apart. Below, the same vulnerable code runs inside an isolated, deny-by-default, capability driven, secure Cosmonic sandbox that only has the exact capabilities needed at execute time. Nothing is patched. Watch both fail anyway.
This is a demonstration of mitigating Remote Code Execution (RCE) type exploits using a secure, deny-by-default, isolated Cosmonic Sandbox.
Try it — fire a real exploit at the sandbox
Each red button streams a genuinely malicious zip 8.6.0 archive into the sandbox. Nothing is patched — watch each one get contained.
| Button | Vulnerability | What the crafted archive does |
|---|---|---|
| Bug 1 | RUSTSEC-2026-0367 · setuid · CVSS 7.3 | Entries carry setuid / setgid / sticky mode bits — on a Unix extractor they would hand a dropped file root-level powers. |
| Bug 2 | CWE-22 / CWE-59 · zip slip via symlinks | Entries are symlinks aimed at known paths outside the extraction directory. |
| Bug 3 | CVE-2026-115905 · zip cloaking · CVSS 10.0 | A benign central-directory name (a scanner clears it) hides the real path a streaming extractor honors from the local header. |
| Run all | all three at once | One archive carrying every attack above, to show the sandbox contains them together. |
.zip here to unzip it in the sandboxWhere to go next
What each of these is for, in plain terms:
zip 8.6.0 as the host demo · not patched (both bugs fixed in 9.0.5) · contained by the sandbox.
cosmonic.com/ai-sandbox
Privacy
Cookies
© 2026 Cosmonic